When a Token Crosses a Network, What Exactly Is Being Verified?
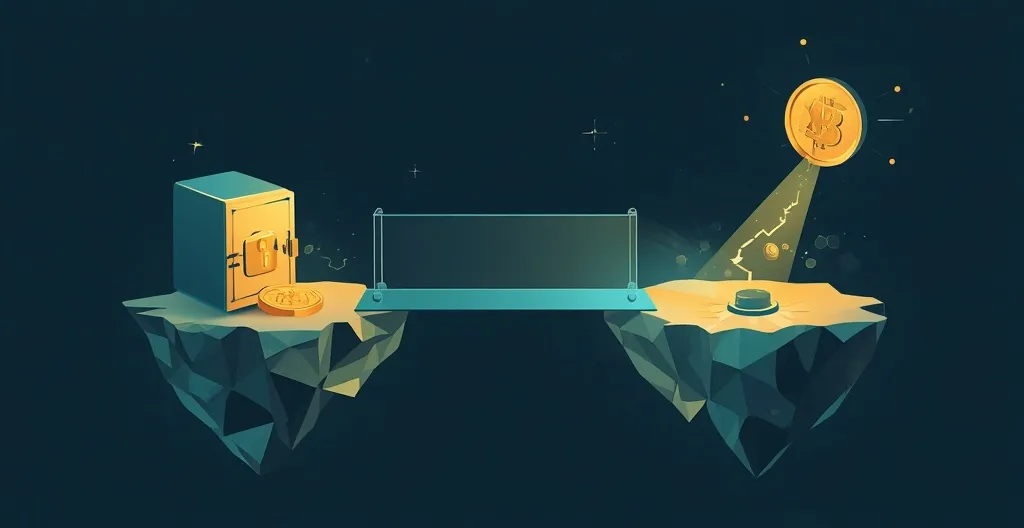
A token doesn’t literally travel from one blockchain to another. A bridge coordinates changes on separate networks, and its verification system decides what evidence the destination-side bridge will accept before it acts.
- Bridges coordinate changes; they do not move tokens between ledgers.
- The verification mechanism provides evidence; the destination chain carries out the action.
- Backing, finality and security assumptions shape the risks.
Each blockchain keeps its own records. Network B has no automatic way to know whether Alice locked or burned tokens on Network A, or whether she was authorized to do so. A bridge links the systems by reporting an event on one network and requesting an action on the other.
The destination chain’s validators generally process transactions according to that chain’s rules. They do not necessarily inspect and verify the source chain themselves. Instead, a bridge’s verification mechanism, which might involve relayers, oracles, operators or a validator set, determines what evidence the destination-side bridge accepts.
So the key question isn’t simply, “Did the token transfer?” It’s this: What evidence does the bridge accept before the destination chain issues or releases value?
Different ways to coordinate a cross-chain transfer
One common approach is lock-and-mint. Say Alice owns 100 tokens on Network A and wants to use them on Network B. The bridge locks her 100 tokens on A, then issues 100 corresponding tokens on B.
The original tokens stay on Network A, but they are meant to remain inaccessible while the destination tokens are in circulation. Those tokens act like receipts for assets held on the source network. If the lock or the bridge’s controls fail and the originals become usable while the corresponding tokens remain active, the system could end up with 200 usable claims against 100 units of value. That’s a possible failure, not an inevitable feature of lock-and-mint.
Burn-and-mint works another way: tokens are destroyed on the source network, then an equivalent amount is issued on the destination network. This avoids relying on a lockbox to hold the original tokens, but verification is still required. The bridge needs evidence that the burn was authorized, involved the right amount and is sufficiently settled before the destination-side action goes ahead.
A liquidity-based model can use assets already available on the destination network. A liquidity provider may send those assets to the recipient, while another process handles settlement or rebalancing between networks. This differs from locking or burning the user’s tokens and issuing a corresponding representation. The source of destination-side liquidity and how the provider gets repaid are separate parts of the arrangement.
What does the bridge actually verify?
A bridge has to decide whether the evidence it receives is enough to act on an event from the source chain. That means more than checking whether a transaction appears in a block. The bridge needs rules for authorization, amount and settlement, along with a way to handle events that are later reversed or disputed under the chain’s rules.
Finality describes when a recorded event is considered settled enough to rely on. In practice, bridges may wait for a chain-specific number of confirmations or follow another settlement rule. There’s no universal threshold. Acting sooner can make transfers faster, while waiting longer can reduce exposure to some reversals.
The evidence mechanism is only one source of risk. In a lock-and-mint design, for instance, the backing assets may sit in a smart contract or be held by a custodian. A flawed contract, compromised keys, weak operational security or social engineering can put those assets at risk, even if the cross-chain message works as intended.
Chainalysis has warned that bridge designs face different attack vectors and recommended measures such as smart-contract audits, security investment and protection against social engineering. The lesson goes beyond “check the proof.” Ask where the backing is held, who controls it, what the verification mechanism trusts and what happens if any of those pieces fail.
Chainlink says its Cross-Chain Interoperability Protocol (CCIP) supports cross-chain data and token transfers. Its CCIP 2.0 documentation describes features such as cross-chain verifiers, configurable settlement speeds and built-in compliance. Those are Chainlink’s descriptions of its product, not independent evidence that any particular implementation is risk-free. The product description also does not establish one token-backing model for every CCIP transfer.
Why real-world assets raise the stakes
For a tokenized financial asset, inconsistent records across networks could complicate claims about ownership, custody, control or supply. Imagine a treasury security represented across five ledgers. If the system is designed to represent the asset on all five, it needs rules to keep the records consistent.
That doesn’t mean every ledger must serve as the legally authoritative ownership register. The record that establishes legal title depends on the asset and jurisdiction. Matching blockchain entries can help coordinate transfers, but they do not settle questions of legal ownership, accountability or recourse on their own.
The Bank for International Settlements’ 2025 Annual Economic Report discusses how tokenization could change how ownership and transfers of claims are recorded. It also stresses the need for public authorities and private actors to cooperate to maintain trust. That’s a useful counterpoint to the idea that putting an asset on a blockchain automatically makes its ownership clear or enforceable.
Bridge losses show why design details matter
In August 2022, after the Nomad Bridge exploit, Chainalysis estimated that $2 billion had been stolen in 13 separate cross-chain bridge hacks. The firm said those attacks accounted for 69% of the funds stolen in 2022 up to that point.
Those figures are an estimate from 2022, not a current cumulative total. They show why bridges shouldn’t be treated as neutral pipes. A bridge’s design determines where assets are held, what evidence is accepted, who or what supplies it, and how the system responds when a critical component fails.
Key questions about cross-chain verification
-
How do bridges transfer value between blockchains?
They coordinate actions on separate networks, such as locking or burning tokens on one chain and issuing or releasing value on another.
-
Who verifies the source-chain event?
It depends on the bridge. Its verification mechanism decides what evidence to accept. The destination chain then carries out the requested action under its own rules.
-
Why can lock-and-mint create duplicate-claim risk?
The destination tokens depend on the original tokens staying inaccessible. If the lock or bridge controls fail and the originals become usable, two claims could exist against the same value.
-
Does burning the source tokens eliminate bridge risk?
No. Burning removes the need to keep those tokens locked, but the bridge still has to verify a valid, authorized burn before issuing an equivalent amount.
-
Does tokenization prove legal ownership?
No. Blockchain records can track claims and transfers, but the legally authoritative record depends on the asset and jurisdiction.
Cross-chain systems rely on independent ledgers acting on a shared account of what happened. Their usefulness depends on the quality of the evidence, the security of the backing and the plan for when something fails.